Search

Announcement

22 posts

Escape's Channel Partners: ConRes, Myriad360, EverSec, Technium, and more

Announcement

Introducing Escape's Channel Partners

After announcing our channel partner program last month, we are excited to now be working with eleven incredible partners, with more soon to join us! Escape's Channel Partner Program is built on a simple principle: a two-way relationship centered on the shared goal of helping security teams do more with the people they have. Our channel partners all play an imperative role in ensuring that these security teams can slot Escape into their security stack and existing workflows to build a continuo

Sanjana Iyer
Escape joins Anthropic’s Cyber Verification Program to advance AI-powered offensive security

Announcement

Escape joins Anthropic’s Cyber Verification Program to advance AI-powered offensive security

Good news doesn't arrive alone. This month we joined not one frontier AI program but two! Yesterday we shared that Escape joined OpenAI's Trusted Access for Cyber. Today we're a verified member of Anthropic's Cyber Verification Program. Both programs solve the same problem. The most useful security research is dual-use by nature. Ask a model to find a broken authorization check and prove it's exploitable, and you've just described an attack. It's the same one a defender runs to close the gap fi

Alexandra Charikova
Escape joins OpenAI’s Trusted Access for Cyber (TAC) to advance AI-powered offensive security

Announcement

Escape joins OpenAI’s Trusted Access for Cyber (TAC) to advance AI-powered offensive security

We've been approved for OpenAI's Trusted Access for Cyber preview. For years we've been building toward one idea: offensive security that runs continuously inside engineering, instead of arriving twice a year as a PDF nobody reads past the executive summary. Business-logic DAST first, then application-layer attack surface management, then Cascade, our AI pentesting agent. Three products on one offensive security engineering platform, because a list of assets, a stream of findings and a pentest

Alexandra Charikova
Escape Honored with Inaugural Wiz Integrations (WIN) Partner Award

Announcement

Escape Honored with Inaugural Wiz Integrations (WIN) Partner Award

Escape has been recognized by Wiz as a winner in the inaugural WIN awards, earning the WINvaluable Award for its outstanding partnership! This recognition highlights Escape's track record of delivering real outcomes for joint customers through the WIN program. 💡Launched in 2023, WIN is Wiz’s open, bidirectional integration ecosystem that now includes over 200 partners — setting a new standard for integrated cloud security. WIN enables prioritized insights from Wiz to flow into partner platfor

Alexandra Charikova
Escape Joins the AWS ISV Accelerate Program to Drive the Future of DAST in Enterprises

Announcement

Escape Joins the AWS ISV Accelerate Program to Drive the Future of DAST in Enterprises

A couple of weeks before the RSA conference, we're thrilled to share that Escape has officially joined the AWS ISV Accelerate Program! This is a huge milestone for us, and it marks an exciting new chapter in our mission to transform how enterprises approach application discovery and dynamic application security testing. The AWS ISV Accelerate Program validates that Escape meets the highest industry standards for security, performance, and compliance. In addition, AWS has recognized our exceptio

Alexandra Charikova
Spring 2025 Events Spotlight

Announcement

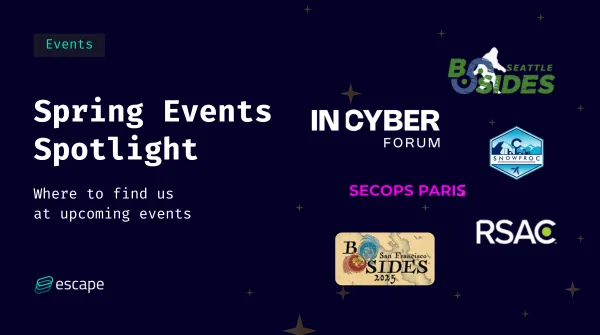
Spring 2025 Events Spotlight

Discover all of the exciting events you can find us at this March and April!

Sanjana Iyer
Join our new Escape community on Slack!

Announcement

Join our new Escape community on Slack!

If you're a security professional who enjoys asking questions, sharing your knowledge with others, and is passionate about API security, this group is for you!

Alexandra Charikova
Introducing Agentless API Discovery & Inventory

Announcement

Introducing Agentless API Discovery & Inventory

Today, we’re finally unveiling new capabilities of Escape - agentless discovery and inventory of APIs within their specific business context.

Tristan Kalos
Escape is now SOC 2 Type II compliant

Announcement

Escape is now SOC 2 Type II compliant

We worked hard to complete the process and get the SOC 2 Type II compliance and finally it's done!

Alexandra Charikova
October Spotlight: The major events not to be missed

Announcement

October Spotlight: The major events not to be missed

If you’re not yet convinced that the fall is the best season to attend cybersecurity conferences, our upcoming event lineup might change your mind! This month, we're taking our team global, from the US to Monaco, Canada to Sweden. Are you planning to soak up the sun and stay by the beach (hello, sunny San Diego 👋 )? Or are you up for a more adventurous journey to explore Montréal? Whatever your choice, we're here and excited to talk with you about all things API security! So, are you ready to

Alexandra Charikova
How we found a security misconfiguration in Philips' GraphQL API

Announcement

How we found a security misconfiguration in Philips' GraphQL API

It is a misconception that discovering vulnerabilities is only within the domain of developers and hackers. Jacob, an Account Executive at Escape, proves this notion wrong. What is a vulnerability disclosure? Vulnerability disclosure is the process of reporting security weaknesses in computer software or hardware. Individuals and groups such as security researchers, IT security teams, and in-house or third-party developers can report these vulnerabilities to the parties responsible for the af

Escape - Offensive Security
Escape and Xolvio officially partner to help teams secure their GraphQL APIs!

Announcement

Escape and Xolvio officially partner to help teams secure their GraphQL APIs!

Keeping APIs secure is vital. However, not all organizations have the in-house resources to tackle it effectively. Xolvio's clients can now leverage Escape's expertise in GraphQL security and performance assessments. They can also integrate it into their CI/CD pipelines, enhancing their API security

Alexandra Charikova
API Security Academy: a smarter way to learn GraphQL security

GraphQL

API Security Academy: a smarter way to learn GraphQL security

Learning about GraphQL security is now more accessible than ever! We're excited to introduce the API Security Academy, developed by the Escape team. Escape's API Security Academy is a free and open-source collection of interactive challenges that will teach you how to secure your GraphQL applications. The challenges are designed to be fun and engaging, and they will help you learn the following: * How to identify and mitigate security vulnerabilities in GraphQL applications * How to apply Gr

Gautier Ben Aïm
September Spotlight: Where to find us at upcoming events

Announcement

September Spotlight: Where to find us at upcoming events

Staying in touch with the cybersecurity community is super important to us. Good news! We're heading to some exciting events in September. Get ready for various talks that are packed with insights and solutions. You're going to walk away ready to tackle any API security challenges that come your way. Our founders and engineers will dive into the chaotic world of GraphQL vulnerabilities. But here's the silver lining - they won't just highlight the problems. They'll also present some smart and p

Alexandra Charikova
Escape raises $3.9 million in seed to secure APIs at every development stage

Announcement

Escape raises $3.9 million in seed to secure APIs at every development stage

Official Press release * Six months after releasing its API security platform, Escape has already secured the applications of 1000+ organizations worldwide and just graduated from Y Combinator. * The funding will allow the company to hire new team members covering European and US-based customers, aiming to double the team’s size in the coming 12 months. If you are interested, take a look at Escape's Open Positions. Paris, Tuesday June 6th 2023 – Escape, the API security company, freshly out

Escape - Offensive Security
The State of Public APIs 2023

Research

The State of Public APIs 2023

tl;dr we scanned 6056+ public APIs on the internet with our in-house feedback driven exploration tech and ranked them using security, performance, reliability, and design criteria. We decided to analyze the resulting data and produce a full featured report: The State of Public APIs 2023 Why build this report? 🤔 Two weeks ago, we released apirank.dev, the result of extensive research on public APIs on the internet, conducted at an unprecedented scale using our feedback-driven API exploration

Escape - Offensive Security
APIRank.dev: we scanned and ranked 6031+ public APIs on the internet

Announcement

APIRank.dev: we scanned and ranked 6031+ public APIs on the internet

tl;dr we scanned 6031+ public APIs on the internet with our in-house feedback driven exploration tech and ranked them using security, performance, reliability, and design criteria. The results are public on APIrank.dev. You can also request to index your own API for free and see how it compares to others. Why APIrank? 🤔 During a YC meetup, I spoke with fellow founder Andrew Kim from Finex. He told me about their struggle to select the right API providers in his past companies. It's true tha

Tristan Kalos
GraphQL Postman Collection: Generate Instantly with GraphMan

Announcement

GraphQL Postman Collection: Generate Instantly with GraphMan

While querying, developing, and testing your GraphQL APIs with postman is easy and convenient, it has a big caveat: if you want to cover an endpoint with all its queries and mutations entirely, it will take you hours and repetitive steps to create every request, and you'll almost surely miss queries, arguments or fields. However, GraphQL APIs can provide their schema, which describes the complete endpoint exhaustively, and this can be exploited for many things: autocompletion, type-safety, etc.

Nohé Hinniger-Foray
Introducing Secure GraphQL for Everyone

Announcement

Introducing Secure GraphQL for Everyone

Find and fix vulnerabilities in your GraphQL applications — powered by Escape's AI-enhanced business logic testing for GraphQL.

Tristan Kalos