Search

Application Security

121 posts

How Amp got its SOC 2 type II pentest evidence in hours

Case Study

How Amp got its SOC 2 type II pentest evidence in hours

Amp is building the AI hiring team for frontline employers. Compliance was in the product from day one, which meant a pentest in year one. Here is how they scoped it, ran it in hours with Escape, and made sure they're ready for their SOC 2 Type II audit.

Alexandra Charikova
Authenticated scanning behind OAuth, MFA, and CAPTCHA

Application Security

Authenticated scanning behind OAuth, MFA, and CAPTCHA

Authenticated vulnerability scanning reaches where your real risk lives, behind the login, and it is the kind of security scanning most tools fail at. A scanner hits the OAuth redirect, the MFA prompt, or the CAPTCHA, falls back to crawling as an anonymous visitor, and still finishes green, so the report says you are covered while the account APIs, admin flows, and tenant boundaries go untested. Authenticated apps break naive scanners in a handful of predictable ways, from OAuth redirects and

Alexandra Charikova
Top continuous penetration testing tools with expert review

AI pentesting

7 best continuous penetration testing tools in 2026

Continuous penetration testing tools close the gap in coverage left by annual pentests. This guide breaks down the best options, what each tool actually does, and how to choose.

Sanjana Iyer
How Escape helped Bridgetech Group replace pentests with automated evidence

Case Study

How Escape helped Bridgetech Group replace pentests with automated evidence

Security scanning that doesn't feel like going to the dentist. See how Bridgetech Group uses Escape for authenticated security testing and API scanning, replacing costly manual pentests with customer-ready security evidence for ISO 27001 and enterprise procurement.

Alexandra Charikova
How Escape AI Pentesting Exploited SSRF in LiteLLM

Agentic Pentesting

How Escape AI Pentesting Exploited SSRF in LiteLLM

At Escape, we routinely test the AI infrastructure that teams deploy inside their cloud environments. LLM gateways, RAG pipelines, model proxies: these are services that make outbound HTTP requests by design, which makes them natural targets for SSRF. When we looked at LiteLLM, we found three confirmed SSRF sinks, a security gate that was specifically built to prevent this exact bug class, and a bypass that means the gate itself is broken. The organization has confirmed to our research team th

Yacine Souam
Escape AI Pentesting Agents 2.0 - A Deep Dive

Application Security

Escape AI Pentesting Agents 2.0 - A Deep Dive

What each agent actually does (BOLA, Regression testing agent, Business logic testing agent, and others..), how they coordinate, and what you can expect from Escape's AI pentesting product in the upcoming weeks.

Alexandra Charikova
Benchmarking AI Pentesting Tools: A Practical Comparison

Application Security

Benchmarking AI Pentesting Tools: A Practical Comparison

We benchmarked 4 AI pentesting tools: Escape, Shannon, Strix, and PentAGI against a modern vulnerable application. Learn more about their detection rates, false positive rates, and scanning speed.

Gwendal Mognier
Top XBOW Alternatives in 2026

Agentic Pentesting

Top XBOW Alternatives in 2026

Escape is the best XBOW alternative for continuous AI pentesting across APIs, web apps, and complex authentication — with regression testing, developer-ready remediation, and platform pricing suited for rapidly scaling orgs.

Alexandra Charikova
Escape vs Burp Suite: The Complete 2026 Comparison

API Security

Escape vs Burp Suite: The Complete 2026 Comparison

Escape is the leading Burp Suite alternative for modern application security teams. Unlike Burp Suite, Escape automates business logic testing (IDORs, SSRFs, access control flaws), ensures faster scanning with fewer false positives, and provides remediation code snippets.

Alexandra CharikovaAntoine Carossio
[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows

Webinar

[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows

Security teams are under constant pressure to do more with the same resources. Manual processes, fragmented tools, and inefficient workflows can slow teams down and pull focus away from what matters most. In this live webinar, experienced security practitioners share how they’ve escaped the constraints of limited resources by rethinking internal workflows, reducing repetitive tasks, and focusing their effort where it matters most. Feeling the pressure to do more with less? Then, this session i

Alexandra Charikova
DAST vs Penetration Testing: Key Differences in 2026

Application Security

DAST vs Penetration Testing: Key Differences in 2026

Learn about the key differences between DAST and pentesting, the emerging role of AI pentesting, their roles in security testing, and which is right for your business.

Alexandra Charikova
Best API security testing tools in 2026: top picks, key features and expert comparison

API Security

Best API security testing tools in 2026: top picks, key features and expert comparison

When it comes to securing applications and APIs, the best API security testing tools are indispensable. These advanced solutions detect vulnerabilities by continuously scanning for weaknesses and simulating real-world attacks. But how do you choose between all API security testing vendors? Agentless API security tools are transforming application security by overcoming the pitfalls of traffic-based solutions like Noname security (part of Akamai) or Salt Security, which burden teams with long s

Alexandra CharikovaAntoine Carossio
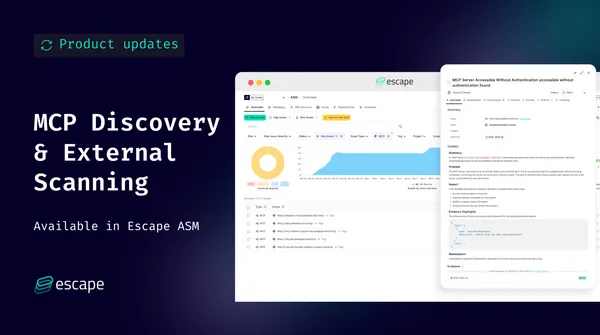
MCP Endpoint Discovery & External Scanning in Escape ASM

Application Security

MCP Endpoint Discovery & External Scanning in Escape ASM

Escape ASM (Attack Surface Management) now natively supports the discovery and external scanning of unauthenticated MCP (Model Context Protocol) endpoints, extending discovery coverage to a new generation of AI-native APIs and LLM infrastructure. As organizations increasingly adopt MCP to connect large language models (LLMs) with tools, data sources, and internal services, new externally exposed attack surfaces are emerging, often without clear visibility or security controls. This update brin

Alexandra Charikova
Apple's App Store Source Map Leak: A Preventable Vulnerability We Found in 70% of Organizations

Application Security

Apple's App Store Source Map Leak: A Preventable Vulnerability We Found in 70% of Organizations

On November 4, 2025, Apple shipped its redesigned App Store website. However, it came with a surprise: JavaScript sourcemaps enabled in production. Within hours, it enabled some to download Apple’s entire front-end codebase directly from the production site. They used a Chrome extension to extract and save all the available resources from the web App Store, and decided to archive them on GitHub for educational purposes. Here's why we're talking about it: with Escape DAST, we've found this exact

Alexandra Charikova