Search

Compliance

8 posts

Compliance penetration testing requirements, by framework

Compliance

Compliance penetration testing requirements, by framework

Which compliance frameworks accept AI pentests? What are the differing requirements across frameworks and what do you need to fulfill them? This is your one-stop guide to being compliance ready before your next audit.

Tristan Kalos
How DAST helps meet Cyber Resilience Act compliance requirements

Compliance

Why DAST Is Critical for Cyber Resilience Act Compliance

The EU’s Cyber Resilience Act is reshaping how companies build and secure digital products. Learn why modern DAST is critical for CRA compliance from secure development to incident response and how to prepare before the 2027 deadline.

Sanjana Iyer
How API Security Fits into DORA Compliance: Everything You Need to Know

Compliance

How API Security Fits into DORA Compliance: Everything You Need to Know

With over 22,000 financial institutions and IT service providers now affected, the Digital Operational Resilience Act (DORA) represents an important shift in cybersecurity for the EU’s financial sector. DORA forces tighter collaboration between regulators, financial institutions, and third-party vendors. It’s not just about protecting internal systems anymore but ensuring the resilience of external digital connections, like APIs, which are the backbone of modern data flows. APIs have become th

Alexandra Charikova
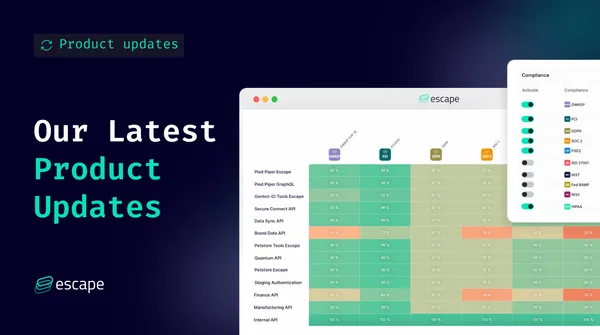
Our Latest Product Updates

Product updates

Our Latest Product Updates

We’re constantly improving our product for our customers. See the latest features, improvements, and fixes we have shipped over the past month. Customize your compliance view Last month we shipped a new feature designed to enhance your compliance management experience. It allows you to hide irrelevant compliance frameworks from your compliance matrix, tailoring it to your organization's specific needs. Don’t care about HIPAA because you are in financial services? You can hide it from yo

Alexandra Charikova
Escape is now SOC 2 Type II compliant

Announcement

Escape is now SOC 2 Type II compliant

We worked hard to complete the process and get the SOC 2 Type II compliance and finally it's done!

Alexandra Charikova
Introducing Seamless GraphQL Compliance

GraphQL

Introducing Seamless GraphQL Compliance

As your go-to partner in GraphQL Security, we at Escape are constantly innovating to simplify and streamline security for you. We're proud of our reputation for crafting modern, dynamic application security testing (DAST) tools tailored to GraphQL, beloved by developers and trusted by security teams worldwide. From comprehensive reporting features and vulnerability checks to seamless CI/CD integrations and remediation assistance, our platform empowers your security teams to ensure robust GraphQL

Antoine Carossio