Search

Events

13 posts

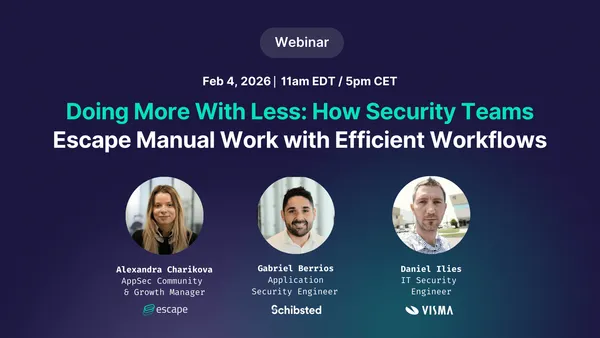
[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows

Webinar

[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows

Security teams are under constant pressure to do more with the same resources. Manual processes, fragmented tools, and inefficient workflows can slow teams down and pull focus away from what matters most. In this live webinar, experienced security practitioners share how they’ve escaped the constraints of limited resources by rethinking internal workflows, reducing repetitive tasks, and focusing their effort where it matters most. Feeling the pressure to do more with less? Then, this session i

Alexandra Charikova
Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap

Application Security

Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap

Two exciting updates in the Elephant in AppSec corner! 1. The Elephant in AppSec Conference 2026 Agenda Is Now Live The agenda for the 2026 edition of The Elephant in AppSec Conference is officially published. This year’s program brings together a lineup of speakers who aren’t afraid to challenge assumptions and share strong, sometimes controversial perspectives on the state of application security. From DevSecOps and security culture shifts to the rising influence of Agentic AI across all a

Alexandra Charikova
[Webinar] From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action

Application Security

[Webinar] From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action

For years, security teams have relied on human penetration testers to uncover critical vulnerabilities hidden in complex business logic. These flaws are subtle, context-dependent, and unique to every system’s workflow. Even modern scanners struggle to capture them, focusing only on a limited range of vulnerabilities displayed in their UI. At Escape, we’ve spent years developing an AI system that goes beyond surface-level issues. It understands application behavior, uncovers vulnerabilities that

Alexandra Charikova
Feedback From Escape Customers: Securing AI-Driven Applications with DAST

Application Security

Feedback From Escape Customers: Securing AI-Driven Applications with DAST

“You ask the developer why they wrote the code the way that they did, and they don’t have an answer anymore. They’re like, ‘Well, AI wrote it.” - Seth Kirschner, DoubleVerify AI is now deeply embedded in software development workflows, and the implications for application security teams are profound. Gone are the days when engineers wrote every line of code themselves, fully understanding the rationale and risks behind each implementation. Today, developers are working side-by-side with tools l

Harikiran Nannapaneni
Webinar: The security mistakes everyone makes in M&A

Webinar

Webinar: The security mistakes everyone makes in M&A

If you often manage security across diverse brands or handle mergers and acquisitions, this webinar is not to be missed, as a panel of guest experts take you through all of the real-world security pitfalls when bringing companies together.

Alexandra Charikova
The Elephant in AppSec Conference: 4 Key Takeaways

The Elephant in AppSec

The Elephant in AppSec Conference: 4 Key Takeaways

Here are the key takeaways from the Elephant in AppSec Conference, uncovering the top insights from industry experts in application security.

Sanjana Iyer
Webinar: How to build relationships with developers

Webinar

Webinar: How to build relationships with developers

Are you a security leader struggling to connect meaningfully with your developers? Join our guest expert, Dustin Lehr, to learn how to earn developers' respect, introduce gamification, and get issues fixed.

Alexandra Charikova
[Webinar] How to secure GraphQL

API Security

[Webinar] How to secure GraphQL

Join Uri Goldshtein and Tristan Kalos for a webinar on GraphQL security and learn to secure your GraphQL APIs.

Tristan Kalos
[Fireside Chat] API sprawl: Understanding the growing challenge of 2024 and how to navigate it

API Security

[Fireside Chat] API sprawl: Understanding the growing challenge of 2024 and how to navigate it

Hey there 👋 Join Bill Doerrfeld, tech journalist and Editor-in-Chief at the Nordic APIs blog, Erik Wilde, OAI Ambassador at the OpenAPI Initiative, and Antoine Carossio, CTO and co-founder at Escape, for a fireside chat on the challenges of API sprawl. Sign me up! During this live discussion, they will explore: * The key factors contributing to API sprawl * Examine its causes * Discuss its implications for organizations, security engineers, and developers * Share insights on ways to pre

Alexandra Charikova
Workshop "How to write custom security tests" - Main Takeaways

API Security

Workshop "How to write custom security tests" - Main Takeaways

Organizations are constantly seeking ways to improve their defenses against business logic vulnerabilities. These vulnerabilities, often difficult to detect, can lead to significant security breaches if left unchecked. To address this challenge, we've introduced a new feature within our platform that empowers teams to create custom business logic tests for APIs, enabling the identification and remediation of security flaws at scale. To explain how to get started with custom security tests, we h

Alexandra Charikova
Webinar: Building Your Product Security Roadmap

Events

Webinar: Building Your Product Security Roadmap

Whether you're in the first few weeks of your ProdSec journey or building your Product security program for 2024, you might feel lost trying to wrap your head around all the attack surface your org faces and identifying some of the biggest security gaps. Don't worry, we're here to help! 💡Missed the live webinar? No problem! Sign up, and you'll receive a recording of the session. Join our webinar with Product Security expert, James Berthoty, and get insights you need to start building a robust

Alexandra Charikova