Search

Product updates

40 posts

Driving efficiency in pentesting: new features live in Escape

Product updates

Driving efficiency in pentesting: new features live in Escape

Offensive security teams are covering more dev teams every quarter without their own headcount growing to match. Their roles continue to be forced into project management and firefighting instead of finding the vulnerabilities that get them speaking spots at conferences. Our latest batch of features removes manual steps that eat away a security engineer's week. Waiting on a full re-run to confirm a fix, manually entering credentials into scan configs, zipping source code over Slack, or chasing

Mitch Mershon
Fix issues with a prompt built for your coding agent

Product updates

Fix issues with a prompt built for your coding agent

There's a translation step between a security finding and a fix, and it's usually done by hand. Someone opens the issue, reads the description, checks the CVSS score, follows the link to the affected asset, works out which endpoint is actually involved, then writes all of it back out as a prompt for whatever agent they code with. The information was already there. It just wasn't in the shape the agent needed. Escape now does that step for you. From any issue in the platform, you can send the

Alexandra Charikova
Escape AI Pentesting Agents 2.0 - A Deep Dive

Application Security

Escape AI Pentesting Agents 2.0 - A Deep Dive

What each agent actually does (BOLA, Regression testing agent, Business logic testing agent, and others..), how they coordinate, and what you can expect from Escape's AI pentesting product in the upcoming weeks.

Alexandra Charikova
Escape Monthly Product Updates — December

Product updates

Escape Monthly Product Updates — December

Discover the latest features we’ve shipped, from multi-tenant testing to enhanced scan failure visibility!

Alexandra Charikova
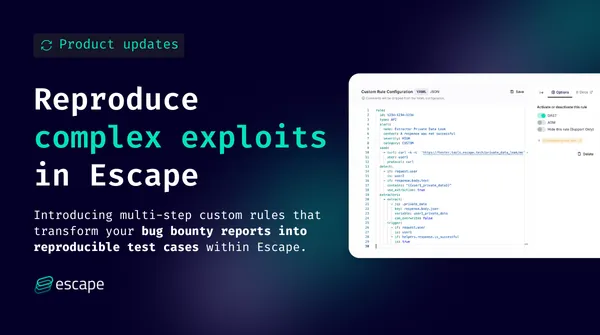
Reproduce complex exploits in Escape: Multi-Step Custom Rules Are Here

Product updates

Reproduce complex exploits in Escape: Multi-Step Custom Rules Are Here

Until now, custom rules in Escape were limited to single-request vulnerabilities. You could only define and test one request at a time. This meant that more complex vulnerabilities, such as those requiring multiple chained steps (e.g., creating a user, then editing that user to escalate privileges), couldn’t be implemented. That changes today. 💡TL;DR: Escape now supports multi-step custom rules. You can chain requests, extract and transform data (tokens, IDs, etc.), and reinject it into subs

Alexandra Charikova
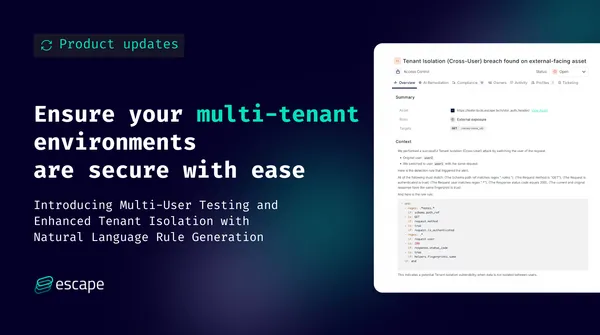
Introducing Multi-User Testing with Natural Language Queries in Escape DAST

Product updates

Introducing Multi-User Testing with Natural Language Queries in Escape DAST

Most of today’s SaaS structures are multi-tenant environments. Making sure that each tenant’s data and resources are securely isolated from others is critical. Weaknesses or misconfigurations in tenant isolation can lead to unauthorized access or data leaks between tenants, compromising the security of the entire system. If you’re serious about maintaining strict isolation and protecting your tenants' data (so you can relax when the Thanksgiving madness hits), this product release is right up y

Antoine Carossio
Introducing AI-Powered Exploit Validation and Remediation Guidelines

Product updates

Introducing AI-Powered Exploit Validation and Remediation Guidelines

Security teams know that finding a vulnerability is only half the battle. The harder part is validating that it can be exploited and applying the right fix with confidence. Too often, remediation guidance is static, generic, or incomplete, leaving engineers guessing. This also strains the relationships between security and developers. As a result, vulnerable applications stay longer exposed to attackers. That’s why we’re introducing AI-powered proof of exploit and remediation guidelines. It sho

Alexandra Charikova
August Product Updates: Enhancements to the Escape Public API and CLI, and the Introduction of Global Configuration Management

Product updates

August Product Updates: Enhancements to the Escape Public API and CLI, and the Introduction of Global Configuration Management

August is usually synonymous with vacations, beach days, and relaxation. But here at Escape, we’re not taking a break from empowering security teams (just kidding, we still took a break, but we shipped more efficiently!). While many are winding down, we’re cranking up the pace with some exciting product updates that will make it easier for you to reduce your organization's risk and streamline your workflows. This month, we’re giving you the ability to modify configurations at the global level,

Alexandra Charikova
More Support for Complex Authentication Flows: TOTP MFA and Text-Based CAPTCHA

Product updates

More Support for Complex Authentication Flows: TOTP MFA and Text-Based CAPTCHA

This June, we’re making it easier to test real-world applications with complex authentication flows without sacrificing automation. Security teams need to test applications exactly as they exist in production, including MFA and CAPTCHA-protected flows. Historically, these protections aren’t "scanner-friendly" and often introduce friction into DAST workflows. With our new TOTP MFA and AI-powered text CAPTCHA solving, Escape now enables fully automated testing on applications protected by these

Alexandra Charikova
From Alert to Action: Escape’s Jira Integration Explained

Product updates

From Alert to Action: Escape’s Jira Integration Explained

Ticketing systems are an essential part of modern DevSecOps. They orchestrate cross-functional collaboration, ensure accountability, and drive issues to resolution. But in application security, the value of ticketing hinges on one critical factor: context. Too often, security tools generate vague alerts or findings without right context associated with them that create noise rather than clarity. Developers are confused with information being fed to them via tickets, which makes the wh

Alexandra Charikova
We now support complex authentication in DAST scans

Product updates

We now support complex authentication in DAST scans

We all know how frustrating the authentication process can be when running DAST scans. It's one of the most common pain points our customers face, and it often becomes a roadblock that slows down testing cycles. Whether it's dealing with complex custom authentication processes or navigating the restrictions imposed by modern web apps, authentication remains one of the trickiest challenges when it comes to using a DAST tool. Imagine this: your current provider only captures the credentials, then

Alexandra Charikova
Kickstart 2025 with New DAST Scanner Features

Product updates

Kickstart 2025 with New DAST Scanner Features

The start of a new year brings exciting updates to our DAST scanner! Our goal is simple: to improve testing accuracy by leveraging real, concrete examples of API requests when they might be required. While we don’t need to have direct access to live traffic to start in-depth testing, we’ve made it easier than ever to import and use traffic examples - giving you better results and more actionable insights (without performance overhead). Here’s a closer look at what’s new: Discover our ne

Alexandra Charikova