Search

Alexandra Charikova

Alexandra leads Growth & Community at Escape and hosts The Elephant in AppSec podcast, focusing on application security. She’s active in BSides Amsterdam, OWASP AppSec Days, and contributes security research featured in outlets like Help Net Security

Alexandra Charikova — Last Publications

Escape vs Burp Suite: The Complete 2026 Comparison

API Security

Escape vs Burp Suite: The Complete 2026 Comparison

Escape is the leading Burp Suite alternative for modern application security teams. Unlike Burp Suite, Escape automates business logic testing (IDORs, SSRFs, access control flaws), ensures faster scanning with fewer false positives, and provides remediation code snippets.


Alexandra CharikovaAntoine Carossio
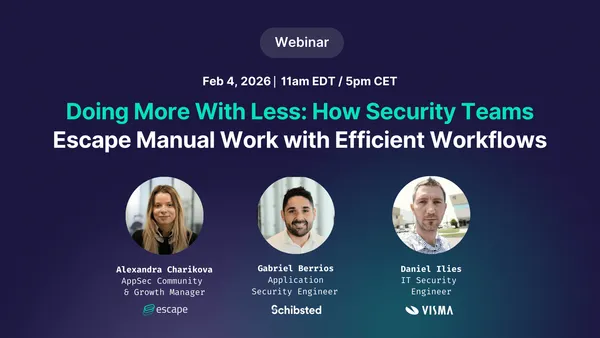
[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows

Webinar

[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows

Security teams are under constant pressure to do more with the same resources. Manual processes, fragmented tools, and inefficient workflows can slow teams down and pull focus away from what matters most. In this live webinar, experienced security practitioners share how they’ve escaped the constraints of limited resources by rethinking internal workflows, reducing repetitive tasks, and focusing their effort where it matters most. Feeling the pressure to do more with less? Then, this session i
Alexandra Charikova
DAST vs Penetration Testing: Key Differences in 2026

Application Security

DAST vs Penetration Testing: Key Differences in 2026

Learn about the key differences between DAST and pentesting, the emerging role of AI pentesting, their roles in security testing, and which is right for your business.

Alexandra Charikova
Best API security testing tools in 2026: top picks, key features and expert comparison

API Security

Best API security testing tools in 2026: top picks, key features and expert comparison

When it comes to securing applications and APIs, the best API security testing tools are indispensable. These advanced solutions detect vulnerabilities by continuously scanning for weaknesses and simulating real-world attacks. But how do you choose between all API security testing vendors? Agentless API security tools are transforming application security by overcoming the pitfalls of traffic-based solutions like Noname security (part of Akamai) or Salt Security, which burden teams with long s

Alexandra CharikovaAntoine Carossio
Top 10 Web Application Penetration Testing Tools (2026)

Pentesting

Top 10 Web Application Penetration Testing Tools (2026)

Explore the best web application penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can support modern web apps with faster, more accurate coverage.

Alexandra Charikova
MCP Endpoint Discovery & External Scanning in Escape ASM

Application Security

MCP Endpoint Discovery & External Scanning in Escape ASM

Escape ASM (Attack Surface Management) now natively supports the discovery and external scanning of unauthenticated MCP (Model Context Protocol) endpoints, extending discovery coverage to a new generation of AI-native APIs and LLM infrastructure. As organizations increasingly adopt MCP to connect large language models (LLMs) with tools, data sources, and internal services, new externally exposed attack surfaces are emerging, often without clear visibility or security controls. This update brin

Alexandra Charikova
Escape vs Bright Security: Full DAST Comparison 2026

Competitor Comparison

Escape vs Bright Security: Full DAST Comparison 2026

Explore how Bright Security differs from Escape, weigh the advantages and disadvantages of both, and determine the best fit for your company.

Alexandra Charikova
Apple's App Store Source Map Leak: A Preventable Vulnerability We Found in 70% of Organizations

Application Security

Apple's App Store Source Map Leak: A Preventable Vulnerability We Found in 70% of Organizations

On November 4, 2025, Apple shipped its redesigned App Store website. However, it came with a surprise: JavaScript sourcemaps enabled in production. Within hours, it enabled some to download Apple’s entire front-end codebase directly from the production site. They used a Chrome extension to extract and save all the available resources from the web App Store, and decided to archive them on GitHub for educational purposes. Here's why we're talking about it: with Escape DAST, we've found this exact

Alexandra Charikova
Best Agentic Pentesting Tools in 2026

Pentesting

Best Agentic Pentesting Tools in 2026

Explore the best Agentic pentesting tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage.

Alexandra Charikova
Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap

Application Security

Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap

Two exciting updates in the Elephant in AppSec corner! 1. The Elephant in AppSec Conference 2026 Agenda Is Now Live The agenda for the 2026 edition of The Elephant in AppSec Conference is officially published. This year’s program brings together a lineup of speakers who aren’t afraid to challenge assumptions and share strong, sometimes controversial perspectives on the state of application security. From DevSecOps and security culture shifts to the rising influence of Agentic AI across all a

Alexandra Charikova
Escape Monthly Product Updates — December

Product updates

Escape Monthly Product Updates — December

Discover the latest features we’ve shipped, from multi-tenant testing to enhanced scan failure visibility!

Alexandra Charikova
Agentic Pentesting: The Complete Guide to Get Started in 2026

Pentesting

Agentic Pentesting: The Complete Guide to Get Started in 2026

Explore this complete guide to agentic pentesting and learn how agentic pentesting architecture works, the key benefits it delivers, and the tools you can integrate into your security workflow.

Alexandra Charikova
best AI pentesting tools

Pentesting

Best 8 AI Pentesting Tools in 2026

Explore the best AI pentesting tools in 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage. Updated: August 2026

Alexandra CharikovaAntoine Carossio
Reproduce complex exploits in Escape: Multi-Step Custom Rules Are Here

Product updates

Reproduce complex exploits in Escape: Multi-Step Custom Rules Are Here

Until now, custom rules in Escape were limited to single-request vulnerabilities. You could only define and test one request at a time. This meant that more complex vulnerabilities, such as those requiring multiple chained steps (e.g., creating a user, then editing that user to escalate privileges), couldn’t be implemented. That changes today. 💡TL;DR: Escape now supports multi-step custom rules. You can chain requests, extract and transform data (tokens, IDs, etc.), and reinject it into subs

Alexandra Charikova
[Webinar] Automating Offensive Security with AI: A Guide to Scaling Pentesting with Escape

[Webinar] Automating Offensive Security with AI: A Guide to Scaling Pentesting with Escape

Automated pentesting is now one of the most hyped topics in cybersecurity, with AI systems promising to replace human hackers. But how much is real, and how much is marketing hype? This webinar provides a practical guide to automating offensive security, built from the perspective of offensive and application security leaders we worked with who’ve spent years pushing the boundaries of what can (and can’t) be automated. We've often heard: "I have only 15 minutes to manually test each new featur

Alexandra Charikova
From Complex Authentication to Confident Coverage: How Applied Systems Transformed Their AppSec with Escape

Case Study

From Complex Authentication to Confident Coverage: How Applied Systems Transformed Their AppSec with Escape

In a recent webinar on "From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action," Andrew Orr Erwing, Manager of Security Engineering (AppSec) at Applied Systems, shared his team's journey in modernizing their application security approach. For organizations that have grown rapidly through acquisitions, application security can become a labyrinth of complexity. Applied Systems found themselves facing this exact challenge—a sprawling tech infrastructure w

Alexandra Charikova
Methodology: How we discovered over 2k high-impact vulnerabilities in apps built with vibe coding platforms

Research

Methodology: How we discovered over 2k high-impact vulnerabilities in apps built with vibe coding platforms

Hey there, With Halloween around the corner, what’s scarier for organizations than vulnerabilities in their web applications? And it's even scarier when the development of these applications is in the hands of users not familiar with security practices. This year, the Escape research team has focused on a growing area of concern: vibe-coded applications. Purpose-built platforms like Lovable.dev, Base44.com, and Create.xyz have democratized application development, enabling non-developers to d

Nohé Hinniger-ForayGwendal MognierAlexandra Charikova
Detectify alternatives in 2026: Escape vs Detectify and 4 more tools

Competitor Comparison

Detectify alternatives in 2026: Escape vs Detectify and 4 more tools

Looking for a Detectify alternative? Compare Escape vs Detectify on API and app security, pricing, G2 ratings, and key features. See why security teams choose this application security scanner for business logic testing and internal app scanning.

Alexandra Charikova
Why context is king in Attack Surface Management (ASM): Key insights from my conversations with security leaders

Attack Surface Management

Why context is king in Attack Surface Management (ASM): Key insights from my conversations with security leaders

When I launched this research, my goal was to understand the current perception of security practitioners regarding Attack Surface Management (ASM) solutions. Unlike in my previous article, "What is wrong with the current state of DAST?" I didn't start with an overall negative perception from the security practitioners. I was just generally curious and asked quite open-ended questions to see if anyone even had strong opinions on ASM (some didn’t!). One key takeaway from the DAST research was th

Alexandra Charikova
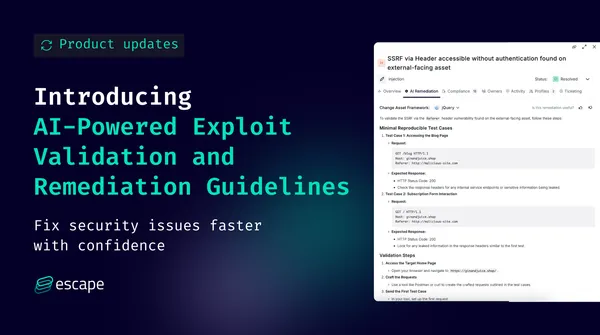
Introducing AI-Powered Exploit Validation and Remediation Guidelines

Product updates

Introducing AI-Powered Exploit Validation and Remediation Guidelines

Security teams know that finding a vulnerability is only half the battle. The harder part is validating that it can be exploited and applying the right fix with confidence. Too often, remediation guidance is static, generic, or incomplete, leaving engineers guessing. This also strains the relationships between security and developers. As a result, vulnerable applications stay longer exposed to attackers. That’s why we’re introducing AI-powered proof of exploit and remediation guidelines. It sho

Alexandra Charikova

Alexandra Charikova — Events, Talks & Papers