Search

Alexandra Charikova

Alexandra leads Growth & Community at Escape and hosts The Elephant in AppSec podcast, focusing on application security. She’s active in BSides Amsterdam, OWASP AppSec Days, and contributes security research featured in outlets like Help Net Security

Alexandra Charikova — Last Publications

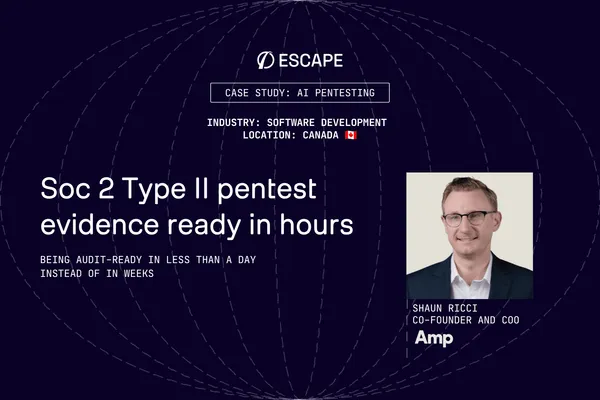
How Amp got its SOC 2 type II pentest evidence in hours

Case Study

How Amp got its SOC 2 type II pentest evidence in hours

Amp is building the AI hiring team for frontline employers. Compliance was in the product from day one, which meant a pentest in year one. Here is how they scoped it, ran it in hours with Escape, and made sure they're ready for their SOC 2 Type II audit.

Alexandra Charikova
Horizon3.ai alternatives

Offensive Security

Horizon3.ai alternatives in 2026: Escape vs NodeZero and 4 more tools

Escape is the best Horizon3.ai alternative for continuous AI pentesting across APIs, web apps, and complex authentication, including regression testing, developer-ready remediation, and platform pricing suited for rapidly scaling orgs.

Alexandra Charikova
escape vs pentera

Offensive Security

Escape vs Pentera: how each one proves exploitability (2026)

Most teams arrive at this comparison with the wrong framing: two automated penetration testing platforms, pick one. Start with what Pentera actually is, because the comparisons that skip this get everything after it wrong. Pentera is an exposure validation platform with a key focus on network testing, and a good one. Pentera Core runs inside your network doing what a red team does in the first week of an engagement: cracking credentials, moving laterally, escalating privilege, testing Active Di

Alexandra Charikova
Pentera Alternatives for Continuous Pentesting: 7 Competitors Compared In-Depth

Offensive Security

Pentera Alternatives for Continuous Pentesting: 7 Competitors Compared In-Depth

Most security and IT teams we talk to who are evaluating Pentera alternatives are mostly happy with what Pentera does. What changed is the shape of the problem underneath them. It used to be a network problem. Now it is also a web application problem, and the tool hasn't kept up with the complexity of modern applications. A manual pentest comes back with a critical on a customer-facing API that the automated pentesting tool never touched, and the uncomfortable part is not the finding itself but

Alexandra Charikova
Escape vs StackHawk: full DAST comparison 2026

Competitor Comparison

Escape vs StackHawk: full DAST comparison 2026

Last updated: August 2026. StackHawk's positioning changed materially in December 2025 with the launch of Business Logic Testing for APIs (Cross-profile BOLA/BFLA only), and again through 2026 with coding-agent integrations. This comparison reflects those changes.

Alexandra Charikova
Authenticated scanning behind OAuth, MFA, and CAPTCHA

Application Security

Authenticated scanning behind OAuth, MFA, and CAPTCHA

Authenticated vulnerability scanning reaches where your real risk lives, behind the login, and it is the kind of security scanning most tools fail at. A scanner hits the OAuth redirect, the MFA prompt, or the CAPTCHA, falls back to crawling as an anonymous visitor, and still finishes green, so the report says you are covered while the account APIs, admin flows, and tenant boundaries go untested. Authenticated apps break naive scanners in a handful of predictable ways, from OAuth redirects and
Alexandra Charikova
Continuous penetration testing: what it means when the testing never stops

Offensive Security

Continuous penetration testing: what it means when the testing never stops

In late 2025, Anthropic disclosed the first documented cyberattack run largely by AI, a state-linked group that used Claude Code to run 80 to 90 percent of an espionage campaign on its own, at thousands of requests a second. Offense now moves at machine speed while most defenses stay scheduled once a year, and closing that gap is what continuous penetration testing is supposed to do, even if it has become a phrase a dozen vendors claim, and almost none define with technical precision. This art

Alexandra Charikova
Escape joins Anthropic’s Cyber Verification Program to advance AI-powered offensive security

Announcement

Escape joins Anthropic’s Cyber Verification Program to advance AI-powered offensive security

Good news doesn't arrive alone. This month we joined not one frontier AI program but two! Yesterday we shared that Escape joined OpenAI's Trusted Access for Cyber. Today we're a verified member of Anthropic's Cyber Verification Program. Both programs solve the same problem. The most useful security research is dual-use by nature. Ask a model to find a broken authorization check and prove it's exploitable, and you've just described an attack. It's the same one a defender runs to close the gap fi

Alexandra Charikova
Escape joins OpenAI’s Trusted Access for Cyber (TAC) to advance AI-powered offensive security

Announcement

Escape joins OpenAI’s Trusted Access for Cyber (TAC) to advance AI-powered offensive security

We've been approved for OpenAI's Trusted Access for Cyber preview. For years we've been building toward one idea: offensive security that runs continuously inside engineering, instead of arriving twice a year as a PDF nobody reads past the executive summary. Business-logic DAST first, then application-layer attack surface management, then Cascade, our AI pentesting agent. Three products on one offensive security engineering platform, because a list of assets, a stream of findings and a pentest

Alexandra Charikova
Best AI DAST tools in 2026: ranked, compared, and reviewed for enterprise security teams

DAST

Best AI DAST tools in 2026: ranked, compared, and reviewed for enterprise security teams

Every DAST vendor put "AI" on the homepage this year. The word now means ten different things to different tools, and even when discussing with analysts, they mention they give an "AI" badge when a certain capability checks the box. This is our attempt to fix that, with a ranked, honest comparison of the AI DAST platforms worth your evaluation time in 2026. Here's what that looks like from the buyer's side: "I am feeling a bit skeptical with the AI across any security vendor and across all the

Alexandra Charikova
Fix issues with a prompt built for your coding agent

Product updates

Fix issues with a prompt built for your coding agent

There's a translation step between a security finding and a fix, and it's usually done by hand. Someone opens the issue, reads the description, checks the CVSS score, follows the link to the affected asset, works out which endpoint is actually involved, then writes all of it back out as a prompt for whatever agent they code with. The information was already there. It just wasn't in the shape the agent needed. Escape now does that step for you. From any issue in the platform, you can send the

Alexandra Charikova
How Escape helped Bridgetech Group replace pentests with automated evidence

Case Study

How Escape helped Bridgetech Group replace pentests with automated evidence

Security scanning that doesn't feel like going to the dentist. See how Bridgetech Group uses Escape for authenticated security testing and API scanning, replacing costly manual pentests with customer-ready security evidence for ISO 27001 and enterprise procurement.

Alexandra Charikova
Escape AI Pentesting Agents 2.0 - A Deep Dive

Application Security

Escape AI Pentesting Agents 2.0 - A Deep Dive

What each agent actually does (BOLA, Regression testing agent, Business logic testing agent, and others..), how they coordinate, and what you can expect from Escape's AI pentesting product in the upcoming weeks.

Alexandra Charikova
Top XBOW Alternatives in 2026

Agentic Pentesting

Top XBOW Alternatives in 2026

Escape is the best XBOW alternative for continuous AI pentesting across APIs, web apps, and complex authentication — with regression testing, developer-ready remediation, and platform pricing suited for rapidly scaling orgs.

Alexandra Charikova
Types of API security testing: a guide for enterprise teams

API Security

Types of API security testing: a guide for enterprise teams

APIs account for a growing share of internet traffic, and attackers have noticed. In 2025, APIs accounted for 17% of all published security vulnerabilities, and 43% of newly added CISA Known Exploited Vulnerabilities were API-related, according to 2026 API ThreatStats Report. Between misconfigured authorization controls, exposed business logic, insecure API integrations, and shadow endpoints that never made it into documentation, the average enterprise API surface presents dozens of entry points

Alexandra Charikova

Alexandra Charikova — Events, Talks & Papers