Product updates
Inside Cascade 2 Iguazu: how we benchmark our AI pentesting engine
How Cascade 2 Iguazu's scheduler and shared coverage map work together, how we benchmark the engine, and what two rounds of internal benchmarks reveal.

Co-founder and CTO of Escape. He worked as a security engineer and penetration tester for Apple and the French National Cybersecurity Agency. A core maintainer of open-source projects like Clairvoyance and a speaker at top security conferences.
Product updates
How Cascade 2 Iguazu's scheduler and shared coverage map work together, how we benchmark the engine, and what two rounds of internal benchmarks reveal.
Agentic Pentesting
Introducing Cascade Iguazu: version 2 of our pentesting engine Cascade. Now with a scheduler-driven multi-agent architecture ensuring consistent, repeatable runs, much wider coverage, and a fully readable trail of what happened.
Offensive Security
Introduction Continuous offensive security testing (COST) is a model for running adversary-style tests whenever something material changes, such as a release, a new internet-facing asset, or a change to a security control. Instead of the standard once a year test, Gartner introduced COST as a term to describe this trigger-driven intelligence-led approach. Escape's evidence standard supports that idea: a finding only counts after it has been reproduced in your own environment, with the requests
AI pentesting
Scanner with a chatbot A real AI pentest Login Stops at the login page Authenticates and tests behind it Identities Tests as one user Holds several at once Findings A list it never reproduced Every one reproduced before it files
AI pentesting
Starts from Asks You get back External pentest The public internet, no access Can an attacker get in at all A demonstrated way in Internal pentest An assumed foothold How far they get once inside A lateral-movement path Vulnerability scan An asset list you supply Is any known issue present A list of possibilities
Pentesting
Introduction An unpatched flaw is now the most common entry point for a breach, at 31%, ahead of stolen credentials at 13%, and the median time to fix one has crept up to 43 days (Verizon's 2026 DBIR). So an annual pentest is always a step behind, and you're two or three people being asked to test continuously with no budget to hire your way there. This is how to build a continuous penetration testing program without hiring more pentesters, by splitting the work so the part that scales runs its
Offensive Security
LLM security testing for pentesters: map attacks to the OWASP LLM Top 10, break a vulnerable MCP server locally, and turn what you find into regression tests. Including solutions for enterprise scale.
Offensive Security
Penetration testing as a service (PTaaS) made buying a pentest almost frictionless. You scope it in a portal, watch findings land on a live dashboard, and click a button to retest the fix, all without a single procurement call. But the test still runs on a schedule, so weeks after it ends you get a report on a version of your app that shipped dozens of releases ago, and everything in between went out untested. PTaaS fixed how you buy a pentest, not when your coverage runs. This guide covers wha
AI pentesting
If you're evaluating AI for offensive security right now, you're weighing two questions at once. The first: why not skip the tooling and point a frontier model at your apps yourself? The second: among the AI pentesting tools you could actually buy, which one earns the budget? We built this benchmark to answer both. Cascade, Escape’s multi-agent AI pentesting engine, went up against a single frontier model (Claude Opus 4.8) driven directly at the same targets. The only variable is the harness ar
AI pentesting
Escape CASCADE allows you to run deep, human-grade assessments across your whole attack surface, proves every finding with a working exploit, and gets more expert in your business with every engagement.

I spent the last week of March 2026 in San Francisco talking to CTOs, CPOs, and engineering leaders from companies of every size about how they actually build with AI agents today. I've met solo founders of pre-series A startups, I attended Y Combinator DevTool Day on March 27 and All Things Dev on March 31, sat down with our advisors, and had dozens of conversations with founders and tool builders working at the frontier. This document is what I brought back. It is a field report: what
Led by Balderton Capital, with participation of Uncorrelated Ventures and existing investors IRIS and Y Combinator, the $18M Series A financing will accelerate our mission to multiply the impact of security teams through full-lifecycle offensive security.

API Security
Escape is the leading Burp Suite alternative for modern application security teams. Unlike Burp Suite, Escape automates business logic testing (IDORs, SSRFs, access control flaws), ensures faster scanning with fewer false positives, and provides remediation code snippets.
API Security
When it comes to securing applications and APIs, the best API security testing tools are indispensable. These advanced solutions detect vulnerabilities by continuously scanning for weaknesses and simulating real-world attacks. But how do you choose between all API security testing vendors? Agentless API security tools are transforming application security by overcoming the pitfalls of traffic-based solutions like Noname security (part of Akamai) or Salt Security, which burden teams with long s
DAST
Discover an in-depth overview of the top 11 DAST tools for 2026, reviewed for APIs, SPAs, and CI/CD pipelines. Compare strengths, weaknesses, and key features that matter to AppSec and DevSecOps teams.
API Security
Testing APIs for Business Logic vulnerabilities is hard. Actually, this is a mission that old-school DAST solutions like ZAP (formerly OWASP ZAP) cannot handle. I'm Antoine Carossio, passionate about Computer Science for more than 15 years now and cofounder & CTO of Escape. With my team, we've spent 3 years building a proprietary algorithm capable of finding Business Logic vulnerabilities in all API types, especially in the most recent ones like REST & GraphQL. However, simply stating its exis
DAST
We ran three scanners against a vulnerable REST API and a vulnerable GraphQL app, comparing findings, request volume, setup time, and scan duration.
Pentesting
Explore the best AI pentesting tools in 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage. Updated: August 2026
Product updates
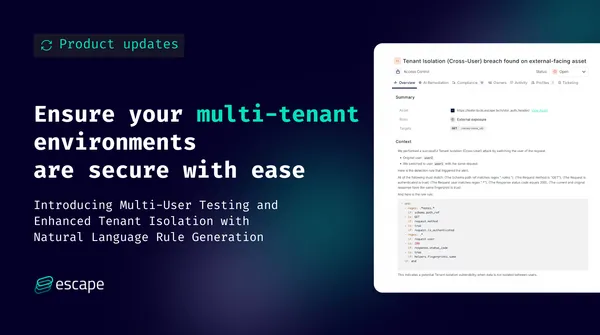
Most of today’s SaaS structures are multi-tenant environments. Making sure that each tenant’s data and resources are securely isolated from others is critical. Weaknesses or misconfigurations in tenant isolation can lead to unauthorized access or data leaks between tenants, compromising the security of the entire system. If you’re serious about maintaining strict isolation and protecting your tenants' data (so you can relax when the Thanksgiving madness hits), this product release is right up y
Application Security
This month, we set out to compare our DAST against some of the established names in Dynamic Application Security Testing. We’ve already benchmarked our scanner on vulnerable apps like VAMPI and DVGA, and now we’re putting it up against Qualys, ZAP, and Intruder (available in free trial) on Gin & Juice Shop. Why are we doing this? Our scanner uses in-house built web crawling and business logic testing algorithms, designed from scratch to handle modern applications. Naturally, we get asked “How d
Pentesting
Explore the best automated penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage.
Application Security
In 2026, vulnerability scanning tools are essential for modern security teams, but running a scan is rarely the hard part anymore. The real challenge is automating it at scale: across thousands of assets, spanning APIs, web applications, and cloud services, in environments that can change by the hour. Security engineers are voicing this exact frustration. You can find it in multiple Reddit threads, like the one below, where a user asked how others automate vulnerability management in
Working with multiple customers implementing DAST in CI/CD has allowed us to learn a lot about what works, what doesn’t, and most importantly how to do it efficiently. The truth is, it’s not about adopting just any tool. It's about making testing for runtime vulnerabilities fit seamlessly into your existing workflow, without slowing things down or creating bottlenecks. The teams that succeed don’t just “plug in” a scanner, hope it works and just checks their box. They adapt their workflows, ch
GraphQL
Last week, the security community was alerted to a vulnerability in Parse Server GraphQL API, which allowed public access to the GraphQL schema without requiring a session token or the master key. It is now identified as CVE-2025-53364. So, the question comes up: Should we disable introspection entirely in production environments to prevent such vulnerabilities? Having heard this question time and time again, I’ve already addressed it in past writings, and my stance remains: Disabling introspe