Search

Alexandra Charikova

Alexandra leads Growth & Community at Escape and hosts The Elephant in AppSec podcast, focusing on application security. She’s active in BSides Amsterdam, OWASP AppSec Days, and contributes security research featured in outlets like Help Net Security

Alexandra Charikova — Last Publications

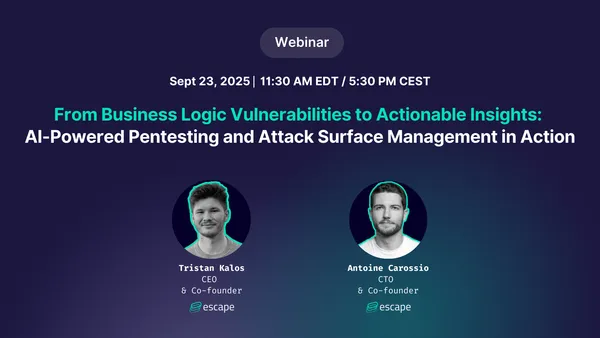
[Webinar] From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action

Application Security

[Webinar] From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action

For years, security teams have relied on human penetration testers to uncover critical vulnerabilities hidden in complex business logic. These flaws are subtle, context-dependent, and unique to every system’s workflow. Even modern scanners struggle to capture them, focusing only on a limited range of vulnerabilities displayed in their UI. At Escape, we’ve spent years developing an AI system that goes beyond surface-level issues. It understands application behavior, uncovers vulnerabilities that

Alexandra Charikova
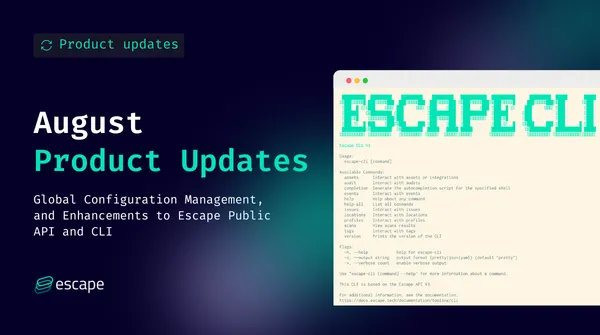
August Product Updates: Enhancements to the Escape Public API and CLI, and the Introduction of Global Configuration Management

Product updates

August Product Updates: Enhancements to the Escape Public API and CLI, and the Introduction of Global Configuration Management

August is usually synonymous with vacations, beach days, and relaxation. But here at Escape, we’re not taking a break from empowering security teams (just kidding, we still took a break, but we shipped more efficiently!). While many are winding down, we’re cranking up the pace with some exciting product updates that will make it easier for you to reduce your organization's risk and streamline your workflows. This month, we’re giving you the ability to modify configurations at the global level,
Alexandra Charikova
Top Automated Penetration Testing Tools (2026)

Pentesting

Top Automated Penetration Testing Tools (2026)

Explore the best automated penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage.

Antoine CarossioAlexandra Charikova
How to Automate Your Penetration Testing?

Application Security

How to Automate Your Penetration Testing?

AI is revolutionizing penetration testing, transforming traditionally manual exploits, once spanning several days, into automated systems that can now handle reconnaissance, scanning, and fuzzing in a matter of hours. Automate your pentesting For teams that deploy every day Book a demo → Learn more "AI is already transforming pentesting. If you look at automated reconnaissance and scanning, finding those low-hanging fruits, or threat intelligence correlation, it does it
Alexandra Charikova
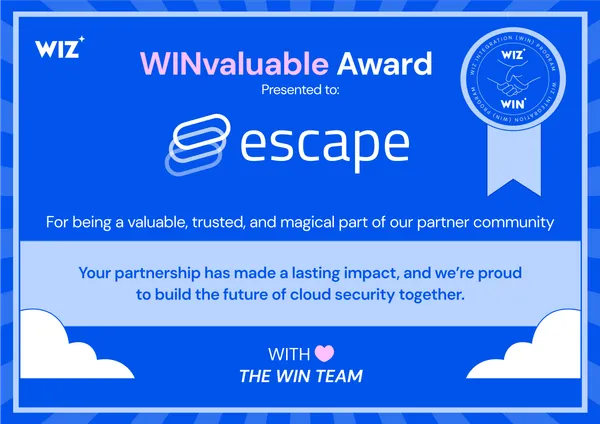
Escape Honored with Inaugural Wiz Integrations (WIN) Partner Award

Announcement

Escape Honored with Inaugural Wiz Integrations (WIN) Partner Award

Escape has been recognized by Wiz as a winner in the inaugural WIN awards, earning the WINvaluable Award for its outstanding partnership! This recognition highlights Escape's track record of delivering real outcomes for joint customers through the WIN program. 💡Launched in 2023, WIN is Wiz’s open, bidirectional integration ecosystem that now includes over 200 partners — setting a new standard for integrated cloud security. WIN enables prioritized insights from Wiz to flow into partner platfor
Alexandra Charikova
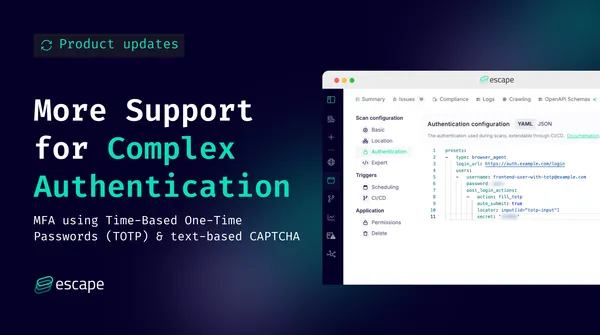
More Support for Complex Authentication Flows: TOTP MFA and Text-Based CAPTCHA

Product updates

More Support for Complex Authentication Flows: TOTP MFA and Text-Based CAPTCHA

This June, we’re making it easier to test real-world applications with complex authentication flows without sacrificing automation. Security teams need to test applications exactly as they exist in production, including MFA and CAPTCHA-protected flows. Historically, these protections aren’t "scanner-friendly" and often introduce friction into DAST workflows. With our new TOTP MFA and AI-powered text CAPTCHA solving, Escape now enables fully automated testing on applications protected by these

Alexandra Charikova
[Webinar] Securing AI-driven applications with DAST

Application Security

[Webinar] Securing AI-driven applications with DAST

Join us for a live webinar with application security experts and Escape clients - Seth Kirschner (DoubleVerify), Nathan Byrd (Applied Systems), Nick Semyonov (PandaDoc), as they break down how their teams are rethinking testing strategies to keep up with AI-influenced codebases.

Alexandra Charikova
From Alert to Action: Escape’s Jira Integration Explained

Product updates

From Alert to Action: Escape’s Jira Integration Explained

Ticketing systems are an essential part of modern DevSecOps. They orchestrate cross-functional collaboration, ensure accountability, and drive issues to resolution. But in application security, the value of ticketing hinges on one critical factor: context. Too often, security tools generate vague alerts or findings without right context associated with them that create noise rather than clarity. Developers are confused with information being fed to them via tickets, which makes the wh
Alexandra Charikova
How Escape Enabled Deeper Business Logic Testing for Arkose Labs

Case Study

How Escape Enabled Deeper Business Logic Testing for Arkose Labs

Arkose Labs is a global cybersecurity company that specializes in account security, including bot management, device ID, anti-phishing and email intelligence. Its unified platform helps the world’s biggest enterprises across industries, including banking, gaming, e-commerce and social media, protect user accounts and digital ecosystems from malicious automation, credential stuffing and other types of online scams and abuse while ensuring legitimate consumers have a safe and seamless experience.
Alexandra CharikovaSanjana Iyer
The Alternative to Acunetix DAST: Escape DAST

Application Security

The Alternative to Acunetix DAST: Escape DAST

Explore how Escape DAST serves as a superior alternative to Acunetix, offering advanced vulnerability detection for web applications and APIs, seamless integration into modern development workflows, and scalable solutions for enterprises.

Alexandra CharikovaAntoine Carossio
Escape Joins the AWS ISV Accelerate Program to Drive the Future of DAST in Enterprises

Announcement

Escape Joins the AWS ISV Accelerate Program to Drive the Future of DAST in Enterprises

A couple of weeks before the RSA conference, we're thrilled to share that Escape has officially joined the AWS ISV Accelerate Program! This is a huge milestone for us, and it marks an exciting new chapter in our mission to transform how enterprises approach application discovery and dynamic application security testing. The AWS ISV Accelerate Program validates that Escape meets the highest industry standards for security, performance, and compliance. In addition, AWS has recognized our exceptio

Alexandra Charikova
We now support complex authentication in DAST scans

Product updates

We now support complex authentication in DAST scans

We all know how frustrating the authentication process can be when running DAST scans. It's one of the most common pain points our customers face, and it often becomes a roadblock that slows down testing cycles. Whether it's dealing with complex custom authentication processes or navigating the restrictions imposed by modern web apps, authentication remains one of the trickiest challenges when it comes to using a DAST tool. Imagine this: your current provider only captures the credentials, then

Alexandra Charikova
How to build a strong business case for replacing legacy DAST with a modern solution - a practical guide

Application Security

How to build a strong business case for replacing legacy DAST with a modern solution - a practical guide

Legacy DAST tools have long been a component in product security programs, but many have become outdated today. Traditional DAST tools were built for yesterday’s web, often providing only basic web scan results and struggling with modern languages like GraphQL or React JS . They tend to be slow, noisy, and used mainly as a compliance checkbox rather than as truly useful tools by security leadership. Luckily, the community's opinion is gradually changing, but updating the legacy DAST solution wi

Alexandra Charikova
Webinar: The security mistakes everyone makes in M&A

Webinar

Webinar: The security mistakes everyone makes in M&A

If you often manage security across diverse brands or handle mergers and acquisitions, this webinar is not to be missed, as a panel of guest experts take you through all of the real-world security pitfalls when bringing companies together.

Alexandra Charikova

Alexandra Charikova — Events, Talks & Papers