




Podcast
Why Your Security Program Might Be Failing Before It Even Starts ⎥ Sean Finley ⎥The Elephant in AppSec Podcast
Discover insights from The Elephant in AppSec episode with Sean Finley.

Podcast
Discover insights from The Elephant in AppSec episode with Sean Finley.
Announcement
Escape has been recognized by Wiz as a winner in the inaugural WIN awards, earning the WINvaluable Award for its outstanding partnership! This recognition highlights Escape's track record of delivering real outcomes for joint customers through the WIN program. 💡Launched in 2023, WIN is Wiz’s open, bidirectional integration ecosystem that now includes over 200 partners — setting a new standard for integrated cloud security. WIN enables prioritized insights from Wiz to flow into partner platfor
Working with multiple customers implementing DAST in CI/CD has allowed us to learn a lot about what works, what doesn’t, and most importantly how to do it efficiently. The truth is, it’s not about adopting just any tool. It's about making testing for runtime vulnerabilities fit seamlessly into your existing workflow, without slowing things down or creating bottlenecks. The teams that succeed don’t just “plug in” a scanner, hope it works and just checks their box. They adapt their workflows, ch

GraphQL
Last week, the security community was alerted to a vulnerability in Parse Server GraphQL API, which allowed public access to the GraphQL schema without requiring a session token or the master key. It is now identified as CVE-2025-53364. So, the question comes up: Should we disable introspection entirely in production environments to prevent such vulnerabilities? Having heard this question time and time again, I’ve already addressed it in past writings, and my stance remains: Disabling introspe
Application Security
“You ask the developer why they wrote the code the way that they did, and they don’t have an answer anymore. They’re like, ‘Well, AI wrote it.” - Seth Kirschner, DoubleVerify AI is now deeply embedded in software development workflows, and the implications for application security teams are profound. Gone are the days when engineers wrote every line of code themselves, fully understanding the rationale and risks behind each implementation. Today, developers are working side-by-side with tools l
Product updates
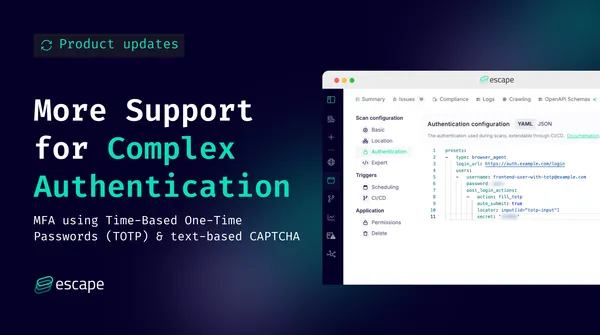
This June, we’re making it easier to test real-world applications with complex authentication flows without sacrificing automation. Security teams need to test applications exactly as they exist in production, including MFA and CAPTCHA-protected flows. Historically, these protections aren’t "scanner-friendly" and often introduce friction into DAST workflows. With our new TOTP MFA and AI-powered text CAPTCHA solving, Escape now enables fully automated testing on applications protected by these
Application Security
In this article, we'll show how we created our web application crawling algorithm to ensure complete testing coverage for modern applications.
Application Security
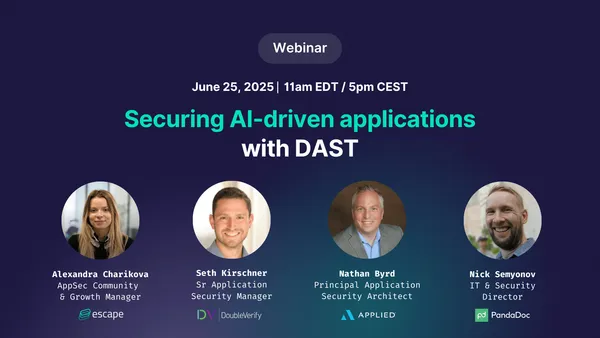
Join us for a live webinar with application security experts and Escape clients - Seth Kirschner (DoubleVerify), Nathan Byrd (Applied Systems), Nick Semyonov (PandaDoc), as they break down how their teams are rethinking testing strategies to keep up with AI-influenced codebases.
Compliance
The EU’s Cyber Resilience Act is reshaping how companies build and secure digital products. Learn why modern DAST is critical for CRA compliance from secure development to incident response and how to prepare before the 2027 deadline.

Product updates
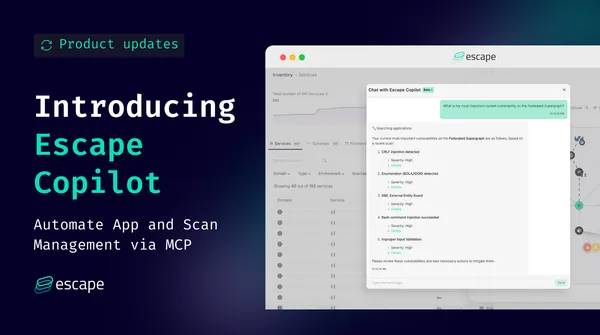
Meet Escape Copilot. Powered by the MCP over the Escape Public API, it helps you boost productivity and get more done with less context switching inside Escape.
Product updates
Ticketing systems are an essential part of modern DevSecOps. They orchestrate cross-functional collaboration, ensure accountability, and drive issues to resolution. But in application security, the value of ticketing hinges on one critical factor: context. Too often, security tools generate vague alerts or findings without right context associated with them that create noise rather than clarity. Developers are confused with information being fed to them via tickets, which makes the wh
Case Study
Arkose Labs is a global cybersecurity company that specializes in account security, including bot management, device ID, anti-phishing and email intelligence. Its unified platform helps the world’s biggest enterprises across industries, including banking, gaming, e-commerce and social media, protect user accounts and digital ecosystems from malicious automation, credential stuffing and other types of online scams and abuse while ensuring legitimate consumers have a safe and seamless experience.
Case Study
Discover how implementing Escape x Wiz integration helped the DoubleVerify AppSec team achieve full API visibility and accelerate targeted remediation.
Application Security
Explore how Escape DAST serves as a superior alternative to Acunetix, offering advanced vulnerability detection for web applications and APIs, seamless integration into modern development workflows, and scalable solutions for enterprises.
Announcement
A couple of weeks before the RSA conference, we're thrilled to share that Escape has officially joined the AWS ISV Accelerate Program! This is a huge milestone for us, and it marks an exciting new chapter in our mission to transform how enterprises approach application discovery and dynamic application security testing. The AWS ISV Accelerate Program validates that Escape meets the highest industry standards for security, performance, and compliance. In addition, AWS has recognized our exceptio
Application Security
Learn from Escape and Wiz’s joint customer, Sr. AppSec Manager Seth Kirschner at DoubleVerify, on how to leverage the Escape x Wiz integration for code-to-cloud security.
Product updates
Escape has created the first ever push-to-post automation to revolutionize vulnerability management by giving you the recognition you deserve.
Product updates
We all know how frustrating the authentication process can be when running DAST scans. It's one of the most common pain points our customers face, and it often becomes a roadblock that slows down testing cycles. Whether it's dealing with complex custom authentication processes or navigating the restrictions imposed by modern web apps, authentication remains one of the trickiest challenges when it comes to using a DAST tool. Imagine this: your current provider only captures the credentials, then
Compliance
If you're responsible for security at a financial services or fintech company, here is your comprehensive overview of what you need to do to be compliant.
Product updates
In addition to our bi-directional Integration with Wiz, we have more product updates for you this month!
Application Security
A new technology partnership enables mutual customers to gain full cloud and application context, establish clear ownership, and accelerate the remediation of critical risks.
Application Security
Legacy DAST tools have long been a component in product security programs, but many have become outdated today. Traditional DAST tools were built for yesterday’s web, often providing only basic web scan results and struggling with modern languages like GraphQL or React JS . They tend to be slow, noisy, and used mainly as a compliance checkbox rather than as truly useful tools by security leadership. Luckily, the community's opinion is gradually changing, but updating the legacy DAST solution wi
Announcement
Discover all of the exciting events you can find us at this March and April!
Webinar recap
Discover exactly how to avoid the common security pitfalls during M&A from our panel of experts, who are drawing from decades of experience in the field.