




API Security
Escape vs Cequence Security: Full 2025 Comparison
Discover why Escape is a better API security solution.

API Security
Discover why Escape is a better API security solution.
The Elephant in AppSec
Learn why CNAPP may be failing security teams and explore the future of cloud security.
Pentesting
This blog is based on our conversation with Harsh Modi, Senior Security Engineer at Bell. It explores what are the benefits of pentesting, and its real-world implications.
Shift left
This blog is based on our conversation with Chris Romeo, founder of Devici, an AI-infused collaborative threat modeling tool. It explores how "shift-left" may be a useful tool in the security toolkit, but it’s far from the only one.
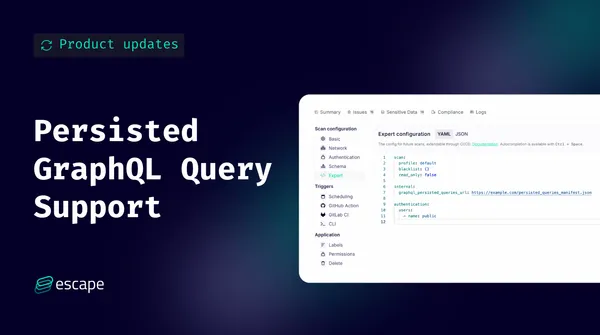
Product updates
You can now test the security of persisted GraphQL Queries with Escape's platform. This new capability enhances our GraphQL API security testing by providing deeper insights into vulnerabilities specific to persisted queries, enabling your team to protect your APIs from targeted attacks better. We support the following formats: * Apollo * Yoga * Custom implementations What are Persisted Queries? Persisted queries in GraphQL help to optimize network performance and enhance security. The c
API Security
Explore how Escape DAST serves as the best alternative to Rapid7, offering advanced vulnerability detection for web applications and APIs, support for complex authentication and seamless integration into modern development workflows.
API Security
Discover how Escape helps implementing API Security faster and with lower overhead than traffic-based solutions like Noname Security.
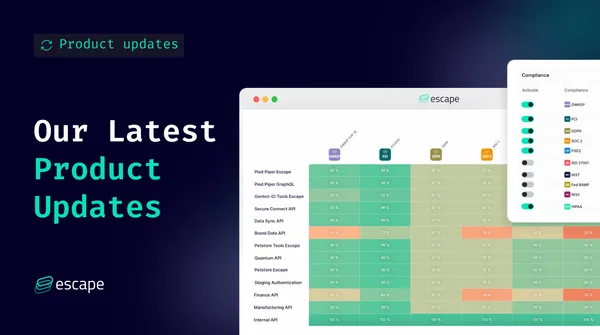
Product updates
We’re constantly improving our product for our customers. See the latest features, improvements, and fixes we have shipped over the past month. Customize your compliance view Last month we shipped a new feature designed to enhance your compliance management experience. It allows you to hide irrelevant compliance frameworks from your compliance matrix, tailoring it to your organization's specific needs. Don’t care about HIPAA because you are in financial services? You can hide it from yo
API Discovery
Discover what makes Escape's agentless API discovery technology truly innovative.
API Security
We have been doing API Security wrong. Discover how the limitations of DAST API security tools might impact your security and why Escape's technology is the best way to protect your APIs.

API Security
We have been doing API Security wrong. Discover how the limitations of traffic-based API security tools might impact your security and why Escape's agentless technology is the best way to protect your APIs.
API Security
Insights from 13,000 GraphQL API issues: Read our deep dive into the current state of GraphQL security.
Podcast
This blog is based on our conversation with Rob van der Veer, Senior Principal Expert at the Software Improvement Group. It explores the complex challenges of developing secure AI systems and the critical role of governance and role segregation in AI security.
Product updates
We are excited to introduce our latest feature: automated schema generation for all your discovered APIs. Having an OpenAPI Specification (OAS) is beneficial because it provides a standardized, machine-readable format for documenting RESTful APIs, promoting clarity and consistency across different services. with an OAS, developers can leverage a plethora of tools for API development, testing, and documentation. It also serves as a contract between API providers and consumers, clearly outlining
API Security
Have you ever wondered how automatic specification generation can streamline API security scanning? By significantly reducing the manual effort involved in creating and maintaining API specifications, automated tools offer clear benefits in terms of scan accuracy and setup time. Yet, many existing tools on the market have notable limitations. Understanding these constraints is essential to fully appreciate how Escape's approach to automated spec generation stands out. Code-first tools C
API Discovery
Discover the role of APIs in the financial sector, and how API discovery ensures security, compliance, and efficiency in financial services.
Data breaches
A recap of Twilio's Authy app breach, which exposed 33 million phone numbers. Including the impacts, lessons learnt and recommendations to enhance your security.
Case Study
Discover how Escape secures the development of the online services of the French Football Federation.
Best Practices
Discover how Escape fits the Kuppinger Cole selection criteria of API Management and Security Solutions.
Webinar recap
Join our guest expert, Dustin Lehr, to learn how to earn developers' respect, introduce gamification, and get issues fixed in a security context.
Product Security
Different models of access control offer unique methods and benefits. The three primary models are Role-Based Access Control (RBAC), Attribute-Based Access Control (ABAC), and Discretionary Access Control (DAC).
Application Security
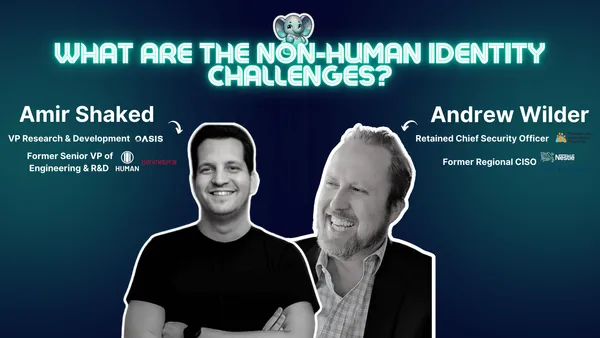
This blog is based on our conversation with Andrew Wilder, Retained Chief Security Officer at Community Veterinary Partners and Amir Shaked, VP of R&D at Oasis Security. It covers the unique challenges of securing non-human identities.
Application Security
Get ready for some opinionated talks.
Application Security
This blog is based on our conversation with Cassie Crossley, Vice President of Supply Chain Security at Schneider Electric. It covers the unique challenges of software supply chain security.